
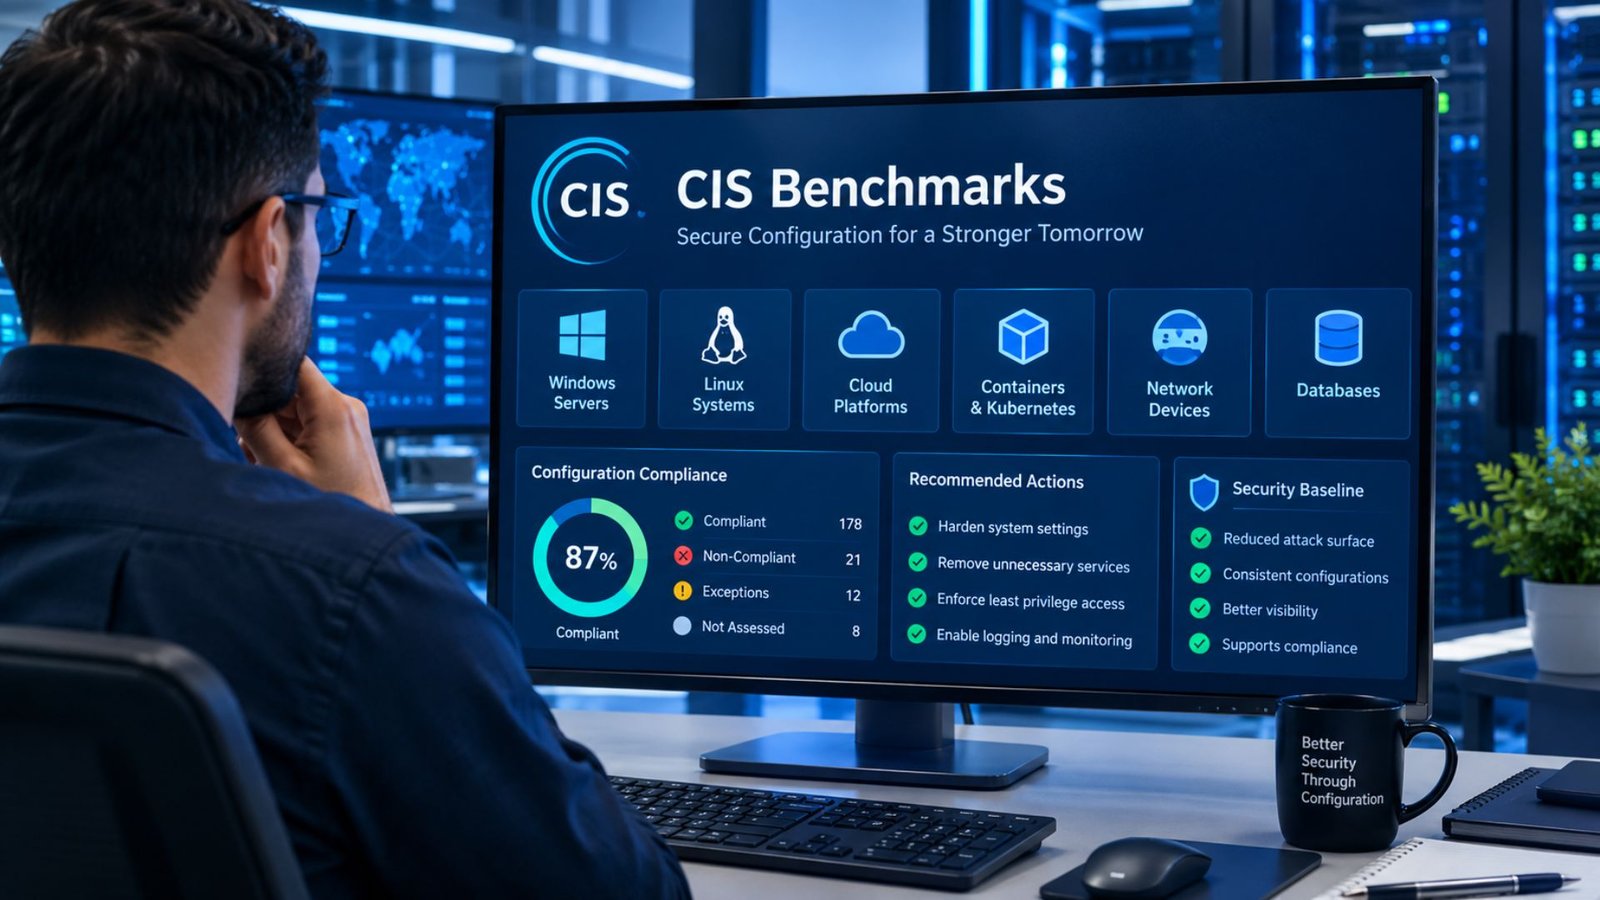
CIS Benchmarks are security configuration recommendations designed to help organizations harden operating systems, cloud platforms, databases, network devices, containers, and other technologies. Developed through a consensus process involving cybersecurity professionals, they provide practical settings that organizations can use to reduce unnecessary exposure and establish a consistent security baseline. The Center for Internet Security (CIS) currently provides more than 100 Benchmarks covering more than 25 vendor product families.
For security teams, system administrators, cloud engineers, and compliance professionals, the real value is not simply following a checklist. The recommendations provide a repeatable starting point for configuring technology more securely and measuring whether systems continue to meet that baseline.
What Are CIS Benchmarks?
CIS Benchmarks are prescriptive, consensus-based guides for securely configuring specific technologies. Instead of providing broad cybersecurity advice, they focus on concrete configuration settings for a particular product, operating system, platform, or service.
The available coverage is broad. CIS lists Benchmarks for cloud providers, operating systems, server software, network devices, desktop applications, mobile devices, databases, DevSecOps tools, and other technology categories. Examples include Microsoft Windows, Linux distributions, Kubernetes, Docker, Cisco devices, Microsoft Azure, Amazon Web Services, Google Cloud, Oracle Cloud Infrastructure, and numerous database platforms.
This specificity matters because secure configuration depends heavily on the technology being protected. A recommendation suitable for a Windows server may not make sense for a Kubernetes cluster or a cloud identity service.
How CIS Benchmarks Improve Security
A default installation often enables features that an organization does not need. Some configurations may also provide more access than required. Hardening reduces these unnecessary exposures by establishing security-focused configuration settings.
CIS Benchmarks can help teams:
- Reduce insecure or unnecessary configurations
- Establish consistent security baselines
- Identify configuration weaknesses
- Support vulnerability and compliance programs
- Improve configuration management across environments
- Create measurable security requirements
- Provide a starting point for system-hardening projects
The recommendations also connect with the broader CIS security ecosystem. CIS states that many Benchmark recommendations map to the CIS Critical Security Controls, creating an on-ramp for organizations working toward broader security and compliance objectives.
Benchmark recommendations are not a universal security solution
A hardened configuration does not eliminate every cybersecurity risk. Organizations still need identity management, patching, monitoring, vulnerability management, incident response, backup strategies, application security, and other controls.
The purpose of a Benchmark is narrower: establish a strong configuration baseline for a specific technology.
CIS Benchmarks vs. CIS Controls
The terms are sometimes confused because both come from the Center for Internet Security, but they serve different purposes.
CIS Controls are a prioritized set of cybersecurity actions intended to help organizations defend against common attack methods. CIS Benchmarks, by contrast, concentrate on secure configuration recommendations for particular technologies.
| Area | CIS Benchmarks | CIS Controls |
|---|---|---|
| Main purpose | Secure technology configuration | Prioritized cybersecurity actions |
| Focus | Specific products and platforms | Organization-wide security practices |
| Example | Harden Windows or Kubernetes settings | Improve account, asset, and security management |
| Primary users | Administrators, engineers, security teams | Security and risk teams |
| Relationship | Provides technical configuration guidance | Provides broader security priorities |
Using both can create a more complete security program: the Controls help determine what security activities should receive attention, while relevant Benchmarks can provide detailed configuration guidance for the technologies involved.
Choosing the Right Benchmark
The correct document depends on the technology and version you are securing. CIS organizes its catalog by technology categories and provides version-specific recommendations.
Before applying a Benchmark, identify:
- The exact product or platform.
- Its version and deployment model.
- Whether it is hosted on-premises, in the cloud, or in a hybrid environment.
- Which Benchmark version applies.
- Which recommendations may conflict with business requirements.
Version control is particularly important. A recommendation written for one operating system release or software version may not apply directly to another. CIS also maintains older versions through its CIS WorkBench resources when appropriate.
💡 Pro Tip:
Create a documented exception process before hardening production systems. If a recommendation cannot be implemented because of an application dependency or operational requirement, record the reason, affected asset, compensating control, owner, and review date instead of silently leaving the setting unchanged.
How to Implement CIS Benchmarks
Implementation works best as a controlled security process rather than a one-time configuration exercise.
Start by creating an inventory of the systems covered by the relevant Benchmark. Then map each recommendation to the actual environment. Some settings may be appropriate for every system, while others may need exceptions because of application dependencies or operational requirements.
Next, test changes in a development or staging environment. This is especially important for servers, databases, network infrastructure, and production applications. A configuration that improves security can still cause availability or compatibility problems if applied without testing.
After validation, deploy approved changes through configuration-management or automation tools where practical. Automated deployment helps reduce configuration drift and makes it easier to maintain the same baseline across multiple systems.
Finally, monitor compliance continuously. New software releases, administrative changes, and infrastructure modifications can gradually move systems away from the approved configuration.
Measuring Compliance and Maintaining the Baseline
CIS provides tools and related resources that can help organizations assess systems against Benchmark recommendations. For example, CIS-CAT Pro can be used to scan systems against applicable secure configuration recommendations.
Measurement should not be treated as a simple pass-or-fail exercise. Security teams should examine failed recommendations and determine whether the finding represents:
- A genuine security weakness
- An approved business exception
- A configuration drift issue
- An outdated assessment
- A recommendation that requires additional validation
The goal is a defensible and continuously maintained security baseline, not an artificially high compliance percentage.
Common Mistakes to Avoid
One common mistake is applying every recommendation without considering the environment. Benchmark guidance should be evaluated against business requirements, application dependencies, performance considerations, and operational constraints.
Another mistake is using an outdated document. CIS regularly publishes updated Benchmark versions, and its catalog shows different versions for individual technologies.
Teams should also avoid treating hardening as a replacement for patch management. Secure configuration and software maintenance address different risks and should work together.
Finally, avoid making manual changes without documentation. Undocumented configuration changes are difficult to reproduce, audit, troubleshoot, or reverse.
📌 Key Takeaway:
CIS Benchmarks give security teams a practical, technology-specific baseline for hardening systems. Their greatest value comes from combining the recommendations with testing, automation, documented exceptions, continuous assessment, and broader security controls.
Frequently Asked Questions
Are CIS Benchmarks free?
CIS provides Benchmark PDFs free for non-commercial use, although users need a CIS account to access the downloads. Organizations can also access additional CIS resources and services through paid offerings such as CIS SecureSuite.
Are CIS Benchmarks a compliance standard?
They can support compliance efforts, but they are not a replacement for every regulatory requirement. CIS explains that Benchmark recommendations can help organizations satisfy secure-configuration requirements found in different regulations and frameworks.
What technologies have CIS Benchmarks?
Coverage includes cloud platforms, operating systems, databases, server software, network devices, desktop software, mobile platforms, DevSecOps technologies, and more. The catalog includes technologies such as Kubernetes, Docker, Windows, Linux, Cisco, Azure, AWS, and Google Cloud.
How often should CIS Benchmark compliance be checked?
There is no universal interval that fits every environment. High-change or high-risk systems may benefit from more frequent assessment, particularly after major configuration or software changes. Continuous or automated assessment can help organizations identify configuration drift sooner.
Do CIS Benchmarks replace CIS Controls?
No. They address different layers of security. CIS Controls provide prioritized cybersecurity actions, while CIS Benchmarks provide detailed secure-configuration recommendations for specific technologies. Using them together can create a stronger and more structured security program.
CIS Benchmarks are most useful when treated as living configuration baselines rather than static checklists. Selecting the correct technology version, testing recommendations before deployment, documenting exceptions, and continuously checking for drift can turn configuration guidance into a practical part of an organization’s security program. For teams responsible for cloud, servers, endpoints, databases, or network infrastructure, that disciplined approach makes secure configuration easier to manage and measure.
Conclusion
CIS Benchmarks give organizations a practical way to establish stronger, technology-specific security configurations. Rather than treating them as a checklist, security teams can use the recommendations as living baselines that support consistent hardening, configuration monitoring, and risk reduction. By selecting the appropriate Benchmark version, testing changes carefully, documenting exceptions, and regularly checking for configuration drift, organizations can make secure configuration a sustainable part of their cybersecurity strategy. For teams managing servers, cloud platforms, databases, networks, and containers, CIS Benchmarks can provide a clear foundation for maintaining more secure environments.
